What is ISO?
Which ISO is Applicable for the Information Security Management System?
Does Your Company Need It?
Often, ISO is understood as an acronym for the International Organization for Standardization. But let us tell you an interesting fact: ISO is not an acronym. The name of the organization changes in different languages. ISO itself unravels the mystery behind this. It says, “Because 'International Organization for Standardization' would have different acronyms in different languages (IOS in English, OIN in French for Organisation internationale de normalisation), our founders decided to give it the short form ISO. ISO is derived from the Greek 'isos', meaning equal. Whatever the country, whatever the language, we are always ISO”.
The International Organization for Standardization (ISO) is an independent non-governmental organization that promotes worldwide proprietary industrial and commercial standards. It develops international standards such as ISO 9001, ISO 14001, etc but does not issue certificates. The ISO certification, which is performed by external certification bodies, is given when the management system, manufacturing system, service or documentation procedure of an organization has all the requirements for standardization and quality assurance.
You may wonder, does my company need an ISO certificate? Well, for companies in some industries, ISO certification is required by law or contractually. Even if that’s not the case, conforming to ISO standards has benefits like
- Saving time and money by identifying and solving recurring problems
- Improving system and process efficiency
- Increasing customer satisfaction
- Being more competitive when tendering for contracts
- Getting more value out of all resources
- Boosting your credibility in the eyes of your customers
The organization has published more than 21,000 standards in areas ranging from quality to food safety management. These standards provide ‘requirements, specifications, guidelines to ensure that materials, products, processes and services are fit for their purpose. Following are few standards relating to Information Security specifically. In particular, the ISO 27001:2022 standard is designed to function as a framework for an organization’s information security management system (ISMS). This includes all policies and processes relevant to how data is controlled and used. ISO 27001:2022 does not mandate specific tools, solutions, or methods, but instead functions as a compliance checklist. In this article, we’ll dive into how ISO 27001:2022 certification works and why it would bring value to your organization.
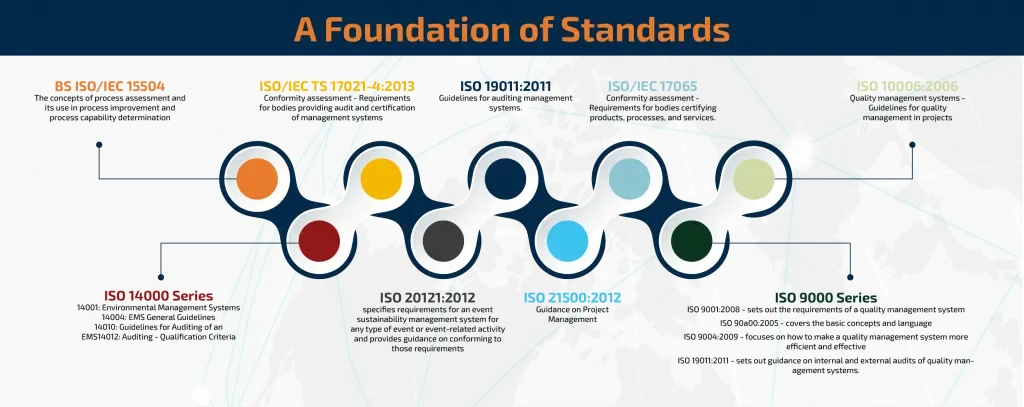
- ISO/IEC 27000 — Information security management systems - Overview and vocabulary
- ISO/IEC 27001 — Information technology - Security Techniques - Information security management systems
- ISO/IEC 27002 — Code of practice for information security controls - essentially a detailed catalog of information security controls that might be managed through the ISMS
- ISO/IEC 27003 — Information security management system implementation guidance
- ISO/IEC 27004 — Information security management — Monitoring, measurement, analysis and evaluation
- ISO/IEC 27005 — Information security risk management
- ISO/IEC 27006 — Requirements for bodies providing audit and certification of information security management systems
- ISO/IEC 27007 — Guidelines for information security management systems auditing (focused on auditing the management system)
- ISO/IEC TR 27008 — Guidance for auditors on ISMS controls (focused on auditing the information security controls)
- ISO/IEC 27009 — Essentially an internal document for the committee developing sector/industry-specific variants or implementation guidelines for the ISO27K standards
For more standards, click on the following link : https://www.iso.org/committee/45306/x/catalogue/p/1/u/0/w/0/d/0
Achieving ISO 27001:2022 certification shows that a business has:
- Protected information from getting into unauthorised hands
- Ensured information is accurate and can only be modified by authorised users
- Assessed the risks and mitigated the impact of a breach
- Been independently assessed to an international standard based on industry best practices
How Did EZ Lab Get Its ISO 27001:2022 Certification?
It is because of our strict approach towards Information Security and Data Protection through measures such as security of physical infrastructure, our policies and procedures and regular personnel training that EZ Labs, our Operations and Innovations hub, was certified with ISO 27001:2022